Master Mobile App Hacking
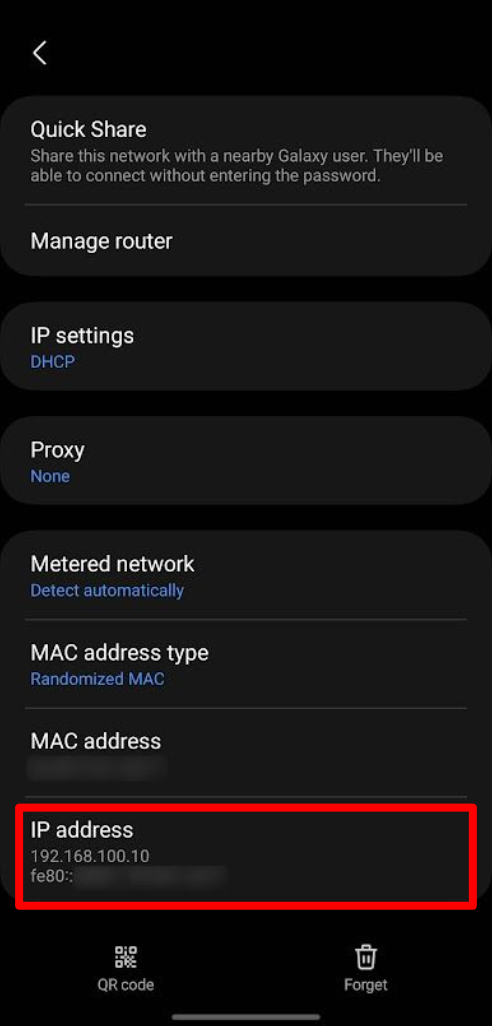
In Proxyman, note the IP address of your Mac (e.g., 192.168.1.10) and the proxy port (default 9090). Enter these into the atlantis- android app: Proxy Host = your Mac's IP , Proxy Port = 9090.

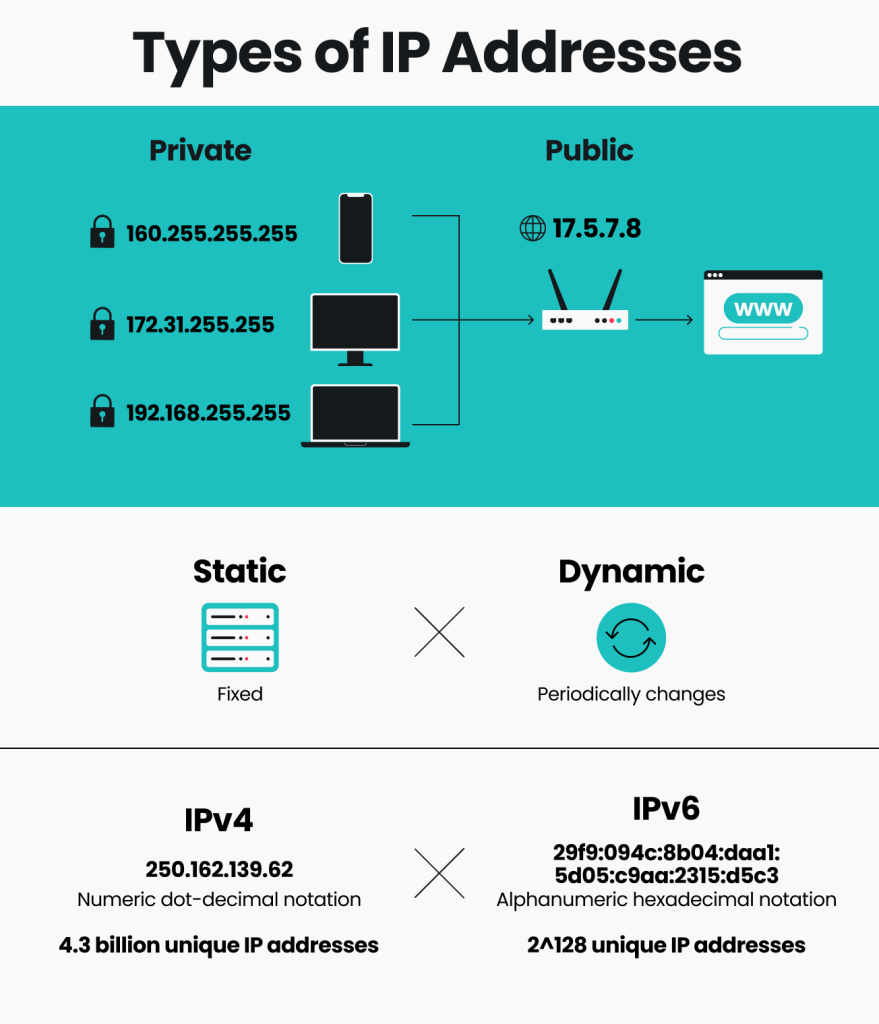
Moving forward, it's essential to keep these visual contexts in mind when discussing Android Intercept Ip Address Snatch.
Step 1: Configure a dedicated proxy listener in Burp To enable Burp to intercept the HTTP traffic generated by your Android device, you need to configure a proxy listener and bind it to an open port. In Burp, open the Settings dialog. Go to Tools > Proxy. Under Proxy Listeners, click Add. On the Binding tab, set Bind to port to any available port. Set Bind to address to All interfaces. Click ...
Set up BurpSuite to listen on a specific IP address and port (default is 8080). This IP will be used as the proxy in the Android device. 4. Configuring the Android Device
A step-by-step walkthrough to intercept and analyze Android app traffic using Genymotion, Burp Suite, and VirtualBox. Ideal for penetration testers, security researchers, and developers working in controlled environments.
Capturing Android App Traffic via Wireshark
Capturing Android app traffic in penetration testing, involves intercepting and analyzing network traffic generated by an Android application. This process helps identify potential security vulnerabilities, such as sensitive data being transmitted without encryption or insecure network communication protocols being used. Pentesters use tools like Wireshark or Burp Suite to capture and analyze ...